
The dark web has become an important subject of study for cybersecurity researchers. Hidden online services can support legitimate privacy-related activities, but some environments are also used for criminal operations involving stolen information, fraud, malware, and other illegal services.
bclub is a name that has appeared in online discussions related to underground carding and payment-card information. Because criminal marketplaces can change domains, disappear, use aliases, or be impersonated by unrelated operators, publicly available claims about a particular site should be approached cautiously.
From a research perspective, the most useful approach is not to focus on accessing an underground marketplace. Instead, researchers can examine what the discussion surrounding bclub.tk reveals about the structure of cybercrime, the lifecycle of underground marketplaces, the challenges of threat intelligence, and the defenses available to organizations and individuals.
Understanding the Dark Web
Before examining any individual marketplace, it is important to understand the terminology.
The surface web consists of websites that conventional search engines can generally index. Public news sites, company websites, blogs, and many online stores belong to this category.
The deep web is much broader. It includes content that is not publicly indexed, such as private databases, subscription services, corporate systems, online banking portals, and password-protected accounts. Most deep-web content is completely legitimate.
The dark web is a smaller portion of the internet that uses technologies designed to provide anonymity or restricted access.
Dark-web technology itself is not inherently criminal. Journalists, researchers, activists, and others may use privacy technologies for legitimate reasons. The legality depends on how those technologies and services are used.
What Is Bclub.tk?
Bclub.tk has been referenced online in connection with discussions about underground carding activity.
A domain name, however, is not enough to establish the identity or legitimacy of a particular service. Underground environments are filled with impersonation, fraudulent listings, abandoned services, and changing infrastructure.
This creates a fundamental challenge for researchers: How can they determine whether an online claim actually represents the organization or marketplace it claims to represent?
The answer involves corroboration.
Researchers can compare multiple independent sources, examine historical records, assess technical indicators, and consider information from established cybersecurity organizations or law-enforcement agencies.
Why Marketplace Research Matters
Studying underground marketplaces can provide valuable insight into cybercrime trends.
Researchers may be interested in questions such as:
- What kinds of information are being targeted?
- Which industries are experiencing increased exposure?
- How are criminals organizing their activities?
- What types of scams are appearing?
- How quickly does compromised information become obsolete?
- How are defensive technologies changing?
These questions can help businesses anticipate threats before they become widespread.
Importantly, responsible research does not require researchers to participate in criminal transactions. Threat intelligence can often be developed from publicly available reporting, technical analysis, historical information, and legally obtained intelligence.
The Connection Between Data Breaches and Underground Markets
Underground marketplaces are often discussed in the context of stolen information.
A data breach can expose information belonging to customers or organizations. Depending on the incident, compromised data may include personal information, login credentials, or payment-related information.
Once information has been exposed, criminals may attempt to monetize it through different channels.
This creates a chain:
Security weakness → data compromise → stolen information → underground activity → attempted fraud.
Breaking any part of this chain can reduce the impact of cybercrime.
Organizations can focus on preventing breaches, while financial institutions can detect suspicious transactions. Individuals can protect accounts with strong authentication and monitor their financial activity.
Carding as a Research Topic
Carding refers broadly to unauthorized activity involving payment-card information.
For researchers, studying carding markets can reveal information about the broader financial-crime ecosystem. Payment-card data may originate from phishing campaigns, malware, compromised accounts, data breaches, or other forms of cybercrime.
The important research question is often not the marketplace itself but the supply chain of compromised information.
Researchers may investigate how information is obtained, how it is advertised or circulated, how long it remains useful, and how financial institutions respond.
This perspective provides a more complete understanding of the threat.
The Problem of False Information
One of the biggest challenges in dark-web research is determining what is real.
Criminal communities can contain scams and misinformation. A marketplace may falsely claim to possess large amounts of stolen data. An unrelated actor may copy the branding of another service. Old information can also continue appearing in search results and social-media discussions.
For this reason, responsible researchers should avoid treating anonymous claims as established facts.
Evidence should be evaluated according to factors such as:
Source reliability: Who published the information?
Independence: Is the claim supported by another source?
Timing: When was the information collected?
Technical evidence: Is there evidence supporting the claim?
Consistency: Does the information match other credible reporting?
This methodology is useful well beyond dark-web research.
Marketplace Lifecycles
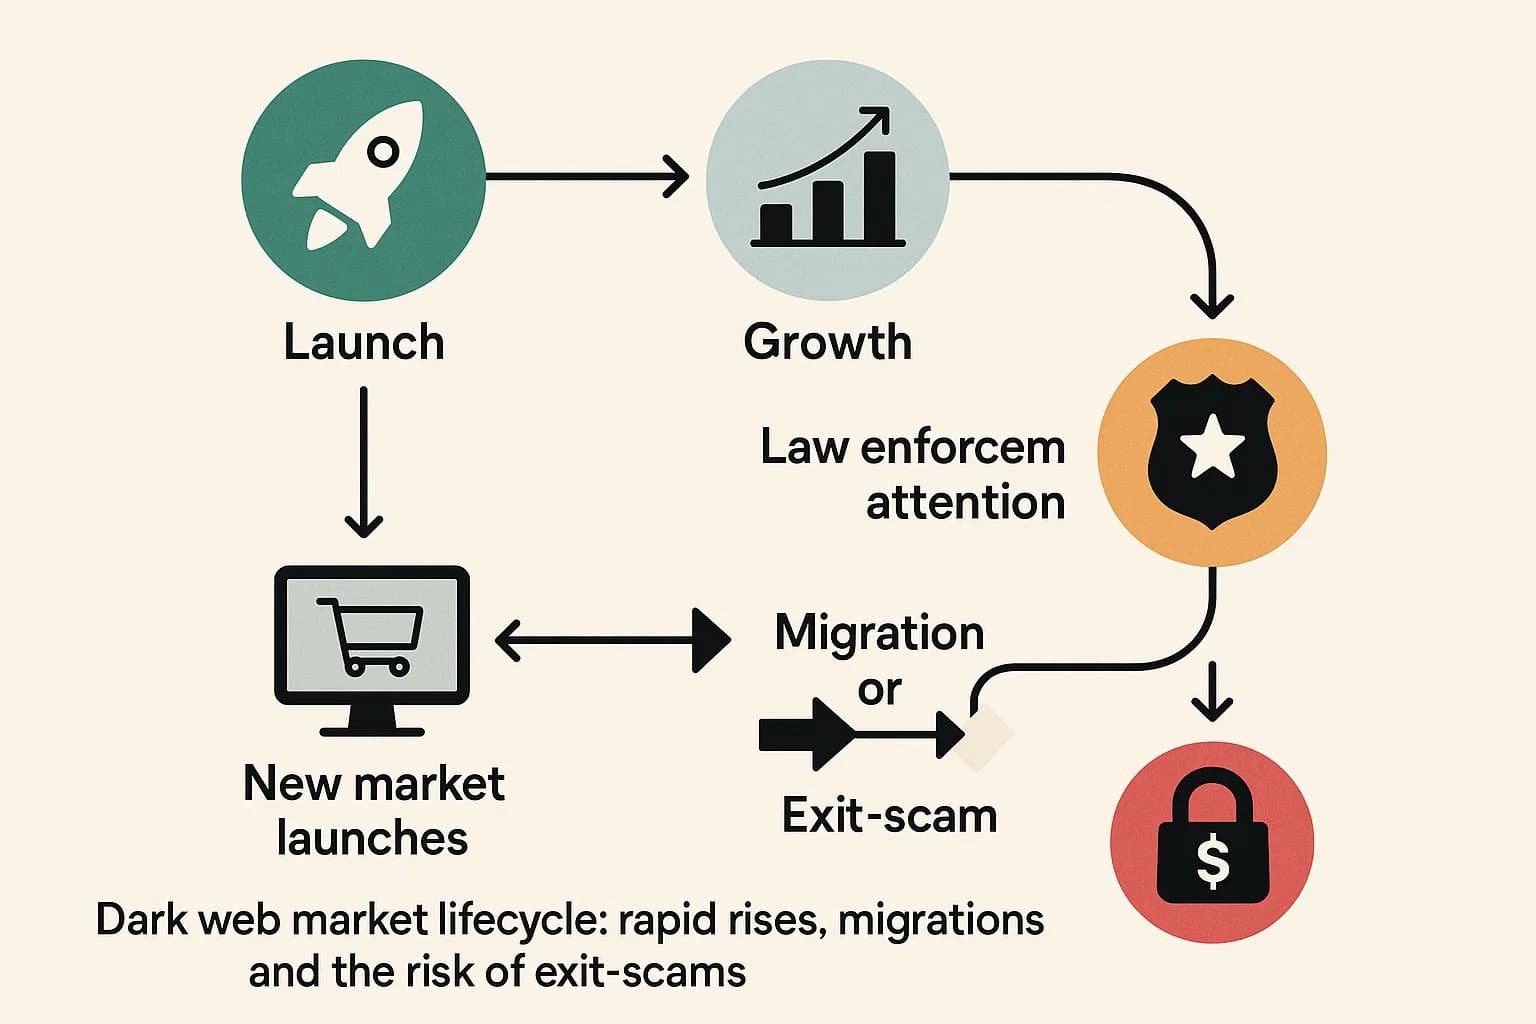
Underground marketplaces can have relatively short lifecycles.
A service may become popular, attract attention, experience internal disputes, suffer technical problems, face scams, or become the subject of law-enforcement action.
When one marketplace disappears, other communities may emerge.
This demonstrates an important characteristic of cybercrime: the ecosystem can be more resilient than individual platforms.
Researchers therefore focus on trends and relationships rather than assuming that eliminating one domain will eliminate an entire category of cybercrime.
The Growing Role of Automation
Automation has changed both cybercrime and cybersecurity.
Criminals can potentially automate repetitive activities, while defenders use automated systems to detect unusual transactions, suspicious logins, malicious files, and abnormal network behavior.
For payment systems, automation is particularly important because large numbers of transactions can occur within a short period.
Modern fraud-detection systems may evaluate behavioral patterns, transaction characteristics, device information, and other signals.
The result is a continuing technological contest between fraudulent automation and defensive automation.
Artificial Intelligence and Dark-Web Research
Artificial intelligence is becoming increasingly relevant to cybersecurity research.
Researchers can use AI tools to analyze large datasets, identify relationships, summarize reports, and assist with threat classification.
At the same time, criminals may attempt to use AI to improve phishing, impersonation, automation, and other malicious activities.
This creates new research questions. Security teams increasingly need to understand not only traditional attack methods but also how automated and AI-assisted activity changes the scale of threats.
How Researchers Study Underground Activity Safely
Ethical cybersecurity research prioritizes legality, privacy, and responsible disclosure.
Researchers can rely on:
- Public threat-intelligence reports
- Security-company research
- Academic studies
- Law-enforcement announcements
- Historical domain information
- Malware analysis
- Anonymized datasets
- Defensive telemetry
When researchers encounter information that may belong to victims, responsible handling is essential. Sensitive information should not be unnecessarily published or redistributed.
The goal is to understand threats while minimizing additional harm.
What Bclub-Related Research Can Teach Defenders
The broader lessons associated with Bclub discussions are relevant to many organizations.
First, sensitive information can have a long lifecycle after a breach.
Second, criminals do not necessarily depend on one platform or domain.
Third, underground markets can contain substantial misinformation.
Fourth, financial fraud is increasingly connected to other forms of cybercrime, including credential theft and social engineering.
Finally, defensive teams need continuous monitoring rather than one-time security assessments.
Protecting Personal and Financial Information
Consumers can take several practical steps to reduce their risk.
Use Unique Passwords
Password reuse increases the potential impact of a compromised account. Unique credentials reduce this risk.
Enable Multifactor Authentication
MFA provides an additional layer of protection beyond passwords.
Monitor Financial Accounts
Regularly reviewing transactions can help identify suspicious activity quickly.
Keep Software Updated
Security patches can address vulnerabilities that criminals might otherwise exploit.
Be Cautious With Phishing Attempts
Unexpected requests for passwords, payment information, verification codes, or account access should be treated carefully.
Contact Your Financial Institution
If payment information may have been compromised, contact the relevant bank or card issuer through an official channel.
What Businesses Should Do
Organizations should combine multiple defensive measures rather than depending on one technology.
Useful controls can include:
- Multifactor authentication
- Strong identity management
- Endpoint protection
- Vulnerability management
- Payment tokenization
- Fraud monitoring
- Threat intelligence
- Employee security training
- Incident-response planning
Businesses should also minimize unnecessary collection and retention of sensitive information.
Reducing the amount of valuable data stored by an organization can reduce the potential impact of a successful breach.
Frequently Asked Questions
Is Bclub.tk still active?
The status of specific underground domains can be difficult to verify reliably. Domains can disappear, change ownership, become inactive, or be impersonated. Claims should therefore be evaluated using current and credible cybersecurity sources.
Does researching the dark web mean accessing illegal websites?
No. Dark-web research can involve public reports, academic studies, technical analysis, and other legally obtained information. Researchers should follow applicable laws and ethical guidelines.
Why are underground marketplaces important to cybersecurity?
They can provide insight into how stolen information is monetized and how different forms of cybercrime connect with one another.
Can underground-market information always be trusted?
No. Anonymous marketplaces and discussions can contain scams, false claims, outdated information, and impersonation.
Conclusion
Exploring Bclub.tk through a cybersecurity research lens reveals a much broader story than any individual domain.
Underground marketplaces are part of a constantly changing cybercrime ecosystem involving data breaches, stolen credentials, payment fraud, malware, social engineering, and increasingly automated activity. The names and platforms involved may change, but the underlying security challenges remain.
For researchers, the priority should be evidence, verification, responsible handling of sensitive information, and a clear distinction between documented facts and unverified claims.
For businesses, the lesson is that cybersecurity requires continuous monitoring, strong identity controls, fraud detection, threat intelligence, and effective incident response.
For consumers, basic security practices remain essential. Unique passwords, multifactor authentication, updated devices, careful handling of unexpected messages, and regular financial monitoring can all reduce exposure.
Ultimately, the value of studying underground marketplaces is not in participating in them. It is in understanding how cybercrime operates at a systemic level so that security professionals can identify threats earlier, organizations can respond more effectively, and individuals can better protect their digital and financial information.
